
When should you choose grey-box testing over black-box testing?
There are three general approaches to penetration testing: black-box, grey-box and white-box. What is the difference between these? Broadly speaking, it comes down to the amount of information, access, data and context provided to the tester at the beginning of the engagement. Each approach has its advantages, but choosing the right one can make a… Continue reading When should you choose grey-box testing over black-box testing?
Beyond Technical Skills: What Makes a Great Penetration Tester?
Beyond Technical Skills: What Makes a Great Penetration Tester? Technical capability is important, but after speaking with experienced penetration testers and seeing what separates good testers from great ones, I think there is a lot more to it than technical knowledge alone. At Red Cursor, we have noticed a few consistent qualities that stand out… Continue reading Beyond Technical Skills: What Makes a Great Penetration Tester?
Why Whitelisting Security Controls Can Lead to a Better Penetration Test
When conducting a penetration test, being asked to whitelist a tester’s IP address from certain security controls might sound counterintuitive. After all, aren’t those controls there to protect the application? They are. But depending on the objective of the penetration test, leaving them in place can actually prevent testers from properly assessing the security of… Continue reading Why Whitelisting Security Controls Can Lead to a Better Penetration Test
Why Are We Still Finding XSS in 2026?
“What is the most common vulnerability you still find in 2026?” It is a question we ask our penetration testers regularly. While Cross-Site Scripting (XSS) may not necessarily be the most common vulnerability we find, it is one that continues to stand out — both because of its potential impact and because, with the maturity… Continue reading Why Are We Still Finding XSS in 2026?
The Voice You Trust Is No Longer Proof
In early 2024, a finance worker at Arup’s Hong Kong office received an email from the company’s UK CFO about a confidential transaction. Something felt off, and he reported it as phishing. Then came the video call. The CFO from the email was on it, plus colleagues he knew – their faces, their voices, talking… Continue reading The Voice You Trust Is No Longer Proof
What has changed in penetration testing over the last 12 months?
Without wishing to jump on the bandwagon, like the rest of the IT world it has to be the large scale adoption of generative AI in all parts of our industry, and even the whole online world. The proliferation in the security environment of AI products is impacting everything from the development and deployment cycle… Continue reading What has changed in penetration testing over the last 12 months?
Using Mimikatz
OverPass-the-Hash Mimikatz can perform the well-known operation “OverPass-The-Hash” to run a process under the security context of another account’s credentials. This is extremely powerful and should not be underestimated. Behind the scenes, Mimikatz requests a Kerberos ticket from the domain controller using the NTLM hash provided. The Kerberos ticket allows authentication to Kerberos services within… Continue reading Using Mimikatz
Penetration Testing Frequently Asked Questions
When is penetration testing required? You have developed an application (in-house or outsourced), purchased an application (commercial off the shelf product), or purchased a software as a service (SaaS) and have concerns or compliance requirements regarding the security of the application or data stored. These concerns can be broadly categorised, in that an adversary or… Continue reading Penetration Testing Frequently Asked Questions
Exploring .git leaks
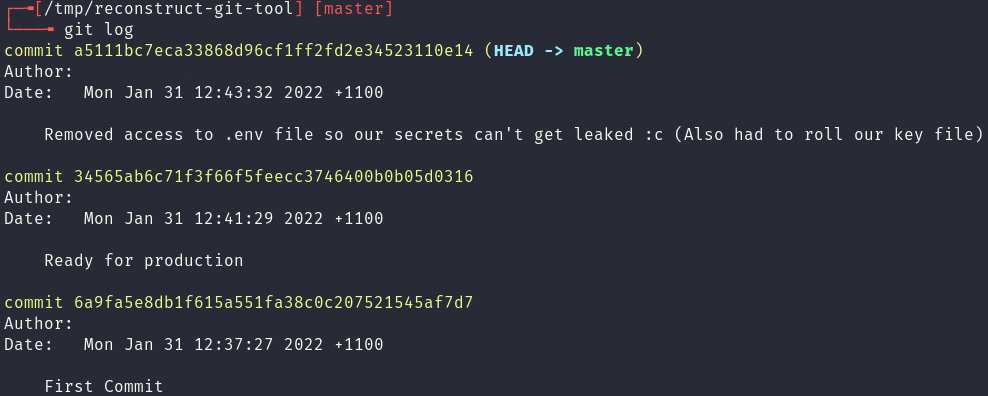
One of the most common mistakes a developer can make, especially when working with technologies like Docker, is copying their .git folder into the web root of their website. This vulnerability usually leads to leaked secrets, credentials and source code. In this blog post Red Cursor will: identify the existence of a .git folder on… Continue reading Exploring .git leaks
Why is penetration testing required?
What is Penetration Testing? Penetration testing, whether it be black box or white box, is a form of risk assessment that aims to identify cybersecurity vulnerabilities and risks within a system. Usually, security is considered a balancing act between confidentiality, integrity and availability. Confidentiality being the ability of the system to keep personal information secret.… Continue reading Why is penetration testing required?